Refrigeration settings were changed remotely in France, then across Europe
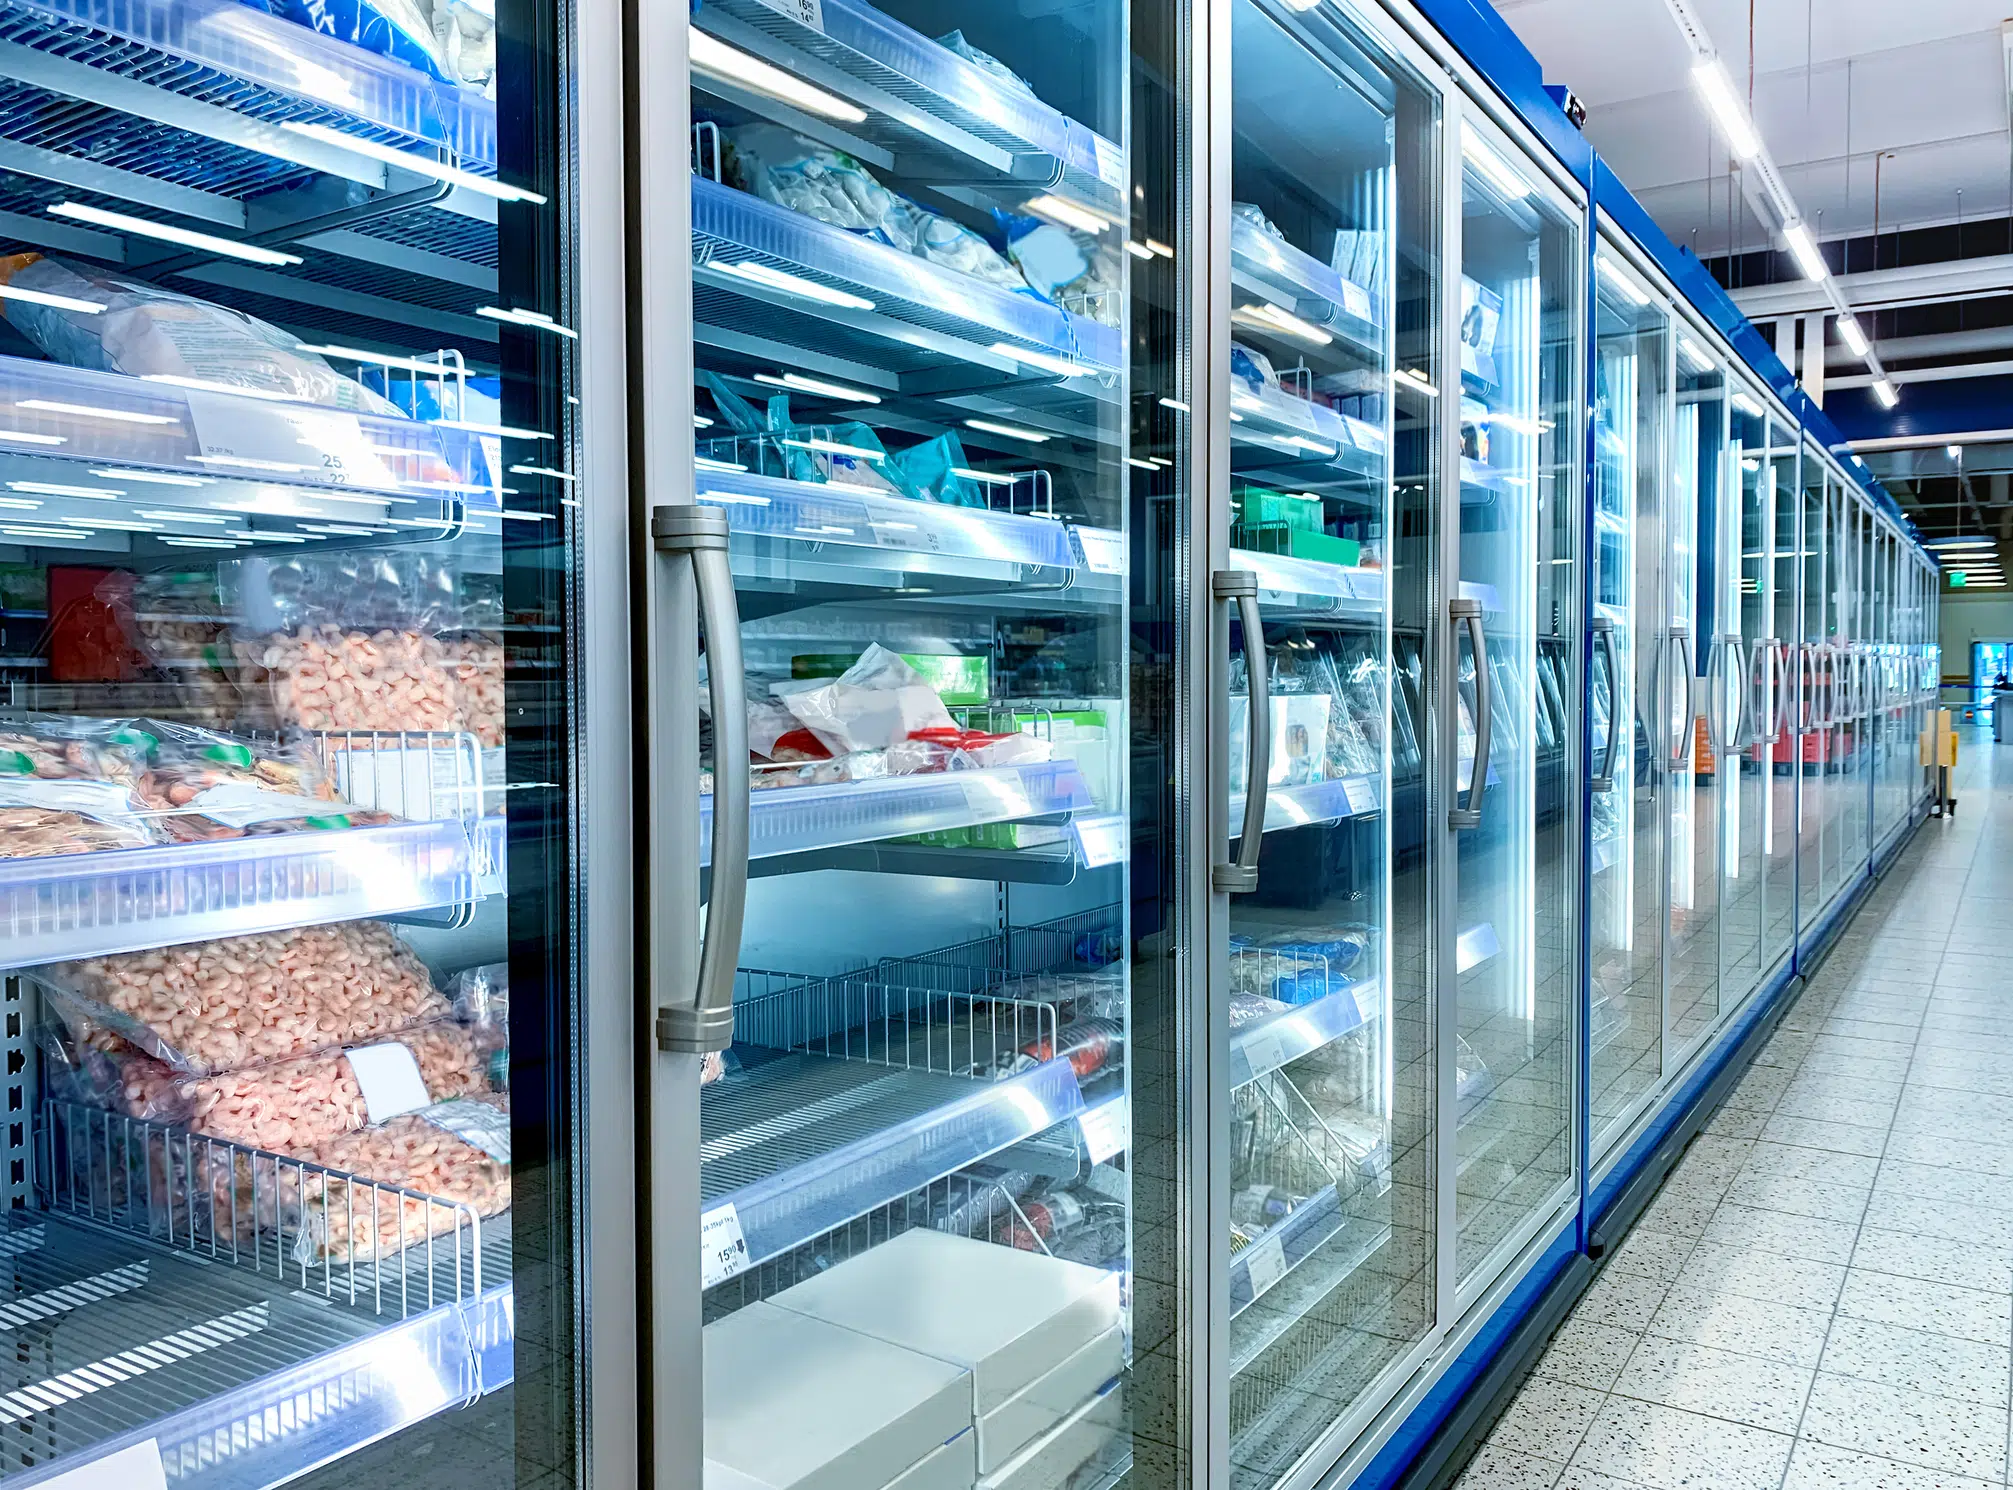
In October 2026, France’s finance minister, Roland Lescure, told Parliament that attacks on refrigeration systems had affected about 700 of the country’s 10,000 supermarkets. The broadcaster BFM-TV reported that attackers forced a continuous defrost cycle and raised temperatures as high as 50°C. The Paris prosecutor’s cybercrime unit is investigating, including the damage from spoiled food and reports of fires.
On 2 November, an Irish supermarket chain removed chilled and frozen food from sale at 13 stores after its monitoring systems detected a problem. The chain later said the incident had been fully resolved, with all stores operating normally and replenishment of chilled and frozen ranges “well under way”. Refrigeration firms in Belgium and Estonia described a method similar to the French one. In Estonia, a refrigeration technology supplier said units at one supermarket had been set to 50°C. By 3 November, AFP reported refrigeration problems in nine countries: Belgium, Estonia, Finland, Ireland, Italy, Luxembourg, the Netherlands, Portugal and Sweden.
On 3 November, BBC News reported that vulnerable refrigeration technology had also been exploited in the UK. Subsequent reporting identified affected businesses elsewhere in the food supply chain, including members of the Association of Independent Meat Suppliers and a fruit and vegetable wholesaler. The National Cyber Security Centre described the national impact as minimal, and the affected meat suppliers reported no loss of food because the units were empty at the time. The UK cases nevertheless extend the reported impact beyond supermarket stores, reinforcing the relevance of secure remote access and up-to-date equipment across the food supply chain.
Read more: BBC News: Fridges in French supermarkets hit by cyber attack; BBC News: UK also affected by cyber-attack which hit European fridges.
In brief
The refrigeration incidents show how remote changes to connected equipment can disrupt a store’s physical operations. They also raise questions that extend beyond refrigeration: which other systems depend on remote access, what infrastructure they share, and how essential functions can continue when something goes wrong.
The Critical Connectivity® Research Series provides a framework for examining those dependencies. It explores how an initially contained fault can affect multiple services, and why the monitoring, access and communications needed for recovery must remain available during the same incident.
In these cases, the reported problem was not a loss of connectivity but unauthorised changes to refrigeration settings. That distinction matters: keeping equipment connected and keeping control of it secure are separate requirements. The incidents provide a starting point for considering both across the connected store.
Refrigeration is one connected system in a store, alongside payment terminals, digital signage, CCTV and building controls. Every remotely managed system in a store raises a similar control question: how authorised users reach it and whether its management interface is exposed unnecessarily. Systems that share one broadband line or router also share a failure domain, creating the separate availability question that the series was built to address. A store estate therefore faces two distinct exposures: how connected systems are controlled and whether they remain available when a shared connection fails. Addressing one does not remove the other, so both need to be covered when retailers review their connected systems.
This commentary applies the series’ framework to the emerging reports, drawing out practical questions for retailers and their contractors. It is separate from the Atlas, the series’ structured record of incidents. These refrigeration incidents have not yet been assessed for inclusion in that record, and the analysis reflects the information currently available.
The reporting establishes three stages of the chain
Of the six stages set out in The Physics of Critical Connectivity Failure, the reporting establishes three for the refrigeration incidents:
- Trigger: the remote changes to refrigeration settings, reported in France as a forced defrost cycle and temperatures as high as 50°C
- Service impact: the impairment of an essential function, the cold chain, with chilled and frozen stock withdrawn or spoiled
- Business consequence: stock disposal, a criminal investigation and reported fires
CERT-FR, the French government’s computer emergency response team, also identifies a potential recovery constraint. Its alert warns that a factory reset alone is insufficient where unsupported equipment stays exposed to the internet, because the device then remains vulnerable and is likely to be compromised again.
That leaves two stages unconfirmed in the public reporting: the shared dependency and the propagation mechanism. Although CERT-FR lists four ranges of remote controllers from three manufacturers, its alert does not name the attackers’ route. Since then, The Hacker News has reported two supplier statements. A controller manufacturer said that affected Dutch systems were not on a secure network and still used default passwords, while an Estonian supplier said that older controllers without updates were targeted. Further detail has since emerged about the French incidents. Sky News reported that the National Cyber Security Centre’s chief executive said the October attacks involved legacy technology connected to the internet with default passwords. This gives a clearer picture of the exposure in France, but does not establish whether the incidents elsewhere involved the same access route or a shared vulnerable system or service.
Because the sources cited here describe no fault spreading between stores, the figure of about 700 French supermarkets measures scale rather than propagation. In the series’ model, the shared dependency and the way disruption spreads through it explain how a problem affecting one component can interrupt several services or sites. Identifying both would help establish whether these incidents followed that pattern.
Read more: The Physics of Critical Connectivity Failure, first edition, October 2026, CERT-FR alert CERTFR-2026-ALE-012
Every remotely managed system raises the same control question
A supermarket’s refrigeration controllers share the building with payment terminals, digital signage, CCTV, building management and, where they are fitted, electronic shelf labels. Different contractors may supply, monitor and update these systems, each with its own arrangements for remote access.
Although CERT-FR’s alert was written for refrigeration controllers, it makes one general point: exposing a management interface on the internet is contrary to good practice. If a device no longer receives security updates and stays exposed to the internet, CERT-FR describes the probability of compromise as very high.
On 2 November, Sweden’s National Cyber Security Centre advised organisations to inventory their internet-connected devices and to consider whether each must be connected. Devices that remain connected, it advised, should be kept up to date and given several layers of security.
Adding a backup connection is only part of protecting a store’s connected systems. If the primary and backup routes rely on the same infrastructure, one fault can affect both. The series captures this principle in its conclusion that “redundancy protects only against the failure domains from which it is independent”.
The same principle applies to remote control. Adding another route may preserve access, but it does not make an existing public interface secure. That exposure remains until the public route is removed or appropriately protected. Removing that public route is CERT-FR’s first recommendation for refrigeration controllers, and the same review can be applied to every system a contractor manages remotely.
Retailers have begun acting on that advice. Reuters reported on 3 November that affected businesses were reviewing exposed equipment, applying updates and restricting direct internet access. The response illustrates the need for a consistent approach across the store estate, including equipment installed and maintained by different suppliers. Protected remote access and managed connectivity can help retailers maintain oversight without requiring every system to be supplied or operated by the same provider.
Read more: NCSC Sweden, 2 November 2026
Systems that share one connection share one failure domain
For a retailer, connectivity disruption can quickly become a trading problem if customers cannot complete their purchases. Payment services were affected in 11 of the 45 incidents analysed in the series’ first edition, counting only cases where an impact on payments was explicitly documented. In the Canadian national operator incident of 2022, more than 12 million customers lost wireless or wireline service, and debit payments, government services and 911 emergency access were disrupted. The series also notes that a device can keep its radio signal while payment authorisation or another platform it relies on is unavailable. A store’s own connection is therefore only one of the dependencies involved in completing a payment.
Research by Retail Economics, produced in partnership with payment technology provider FreedomPay, has estimated the potential exposure for UK retail and hospitality. Measured as sales at risk rather than recorded losses or lost profit, total payment disruption exposure came to £1.681 billion in 2025. It attributed £397 million of that figure to network or internet outages. On those two figures, outages account for about 24 per cent of the total.
A store’s payment terminals, signage and CCTV may share one broadband line and router. That creates two questions: what keeps these systems connected if the link fails, and what controls protect access to each system? An independent backup connection can address the first. The second requires appropriate separation between systems and remote access restricted to authorised users. Both matter: an alternative connection can preserve availability, but it does not by itself prevent unauthorised access or changes to equipment settings.
Source report: Retail Economics and FreedomPay: Payment Resilience in Retail and Hospitality
Monitoring has to survive a compromised controller
Restoring a service depends on being able to see what has gone wrong, reach the affected equipment and make the necessary changes. Those capabilities can themselves be disrupted: in 27 of the 45 incidents analysed in the series’ first edition, the monitoring, access, credentials, data or communications needed for restoration were affected. For refrigeration systems, recovery may also depend on whether a compromised controller can be returned to secure operation, rather than simply reset and reconnected.
CERT-FR’s advice is to remove direct public internet access to refrigeration controllers and provide any necessary remote access through a secure virtual private network (VPN) or protected network. The aim is not to stop contractors monitoring and maintaining equipment remotely, but to ensure that they reach it through a controlled connection rather than an exposed management interface.
Making that change requires coordination between the retailer and its refrigeration contractor. They should identify which connections support temperature reporting, alarms and maintenance, and agree how those functions will continue through the protected route. The alert also advises operators to check their insurance terms before interrupting data uploads to a contractor. The practical objective is to reduce exposure without losing the visibility and alerts needed to protect stock, with monitoring and remote access checked after the change.
When equipment settings are changed unexpectedly, reliable monitoring helps operators identify the problem and decide how to protect stock. The Irish chain’s monitoring systems detected the issue, prompting the precautionary withdrawal of chilled and frozen products. The series highlights a further requirement: monitoring should remain available and trustworthy even when the equipment or service it oversees is affected.
Reliable monitoring also depends on where the readings come from. If the same controller manages cooling and reports temperatures, compromising it could affect both functions. A separate means of checking temperatures can help operators establish what is happening inside the cabinet.
Bringing security and resilience together across the store estate
Individual systems may be managed by different contractors, but retailers need a clear view of how the connections supporting them work together. A payment provider, refrigeration contractor or CCTV installer may understand its own equipment without having visibility of the dependencies shared across the store.
The practical task is therefore to look beyond each system in isolation and consider:
- how contractors reach equipment remotely, and how that access is protected
- which systems share a connection, router or provider, and what happens if it becomes unavailable
- whether alternative connections are independent of the infrastructure they are intended to back up
- how monitoring, alarms and essential services continue during disruption.
These questions bring the discussion beyond individual equipment contracts to the design and management of the connectivity layer. This is where CSL can work alongside retailers and their existing technology partners, helping to bring protected remote access, resilient connections and ongoing connectivity monitoring together across the estate.
The aim is not to replace every system or supplier, but to ensure that the connections supporting them are designed and managed as part of a coherent approach to security and continuity.
How CSL supports secure and resilient store connectivity
CSL brings this approach to the connectivity layer, combining managed connections, protected remote access and resilience options to support the systems already deployed across a store estate.
CSL provides managed connectivity for critical IoT and safety applications, supporting more than 3.5 million active direct connections through fully managed single or multi-path services. Its alarm signalling products and services carry fire and security signalling to more than 270 alarm receiving centres (ARCs) across Europe.
To help reduce control exposure, CSL’s IoT SIMs can use private APNs to provide connectivity that is isolated from the public internet. A CSL router can also combine private cellular connectivity with private broadband, depending on the site’s configuration and requirements. Where remote management is restricted to authorised users over protected private connections, management interfaces do not need to be exposed directly to the public internet.
For service availability, CSL Router configurations include fixed broadband with cellular failover. Mobile connectivity can also use CSL DualCore® architecture to provide independent operator-core paths. CSL’s rSIM® brings this resilience into a single SIM, with built-in connectivity testing and automatic switching to a second operator profile if a persistent connection failure is detected. This helps restore connectivity even where a device still shows a mobile signal but can no longer pass data.
CSL manages and monitors the connectivity layer, working alongside the retailer and its contractors, who retain responsibility for the connected systems, firmware and user permissions.
To discuss connectivity across a store estate, contact sales@csl-group.com.
This commentary draws on reporting and guidance available as at 4 November 2026. Further details may emerge as investigations continue.